Why Teachers Fall for Phishing: 6 School Reasons
When you know your staff is smart, kind, and stretched thin, seeing teachers fall for phishing can feel personal. The better question is not why a teacher clicked, but what made that fake email feel…
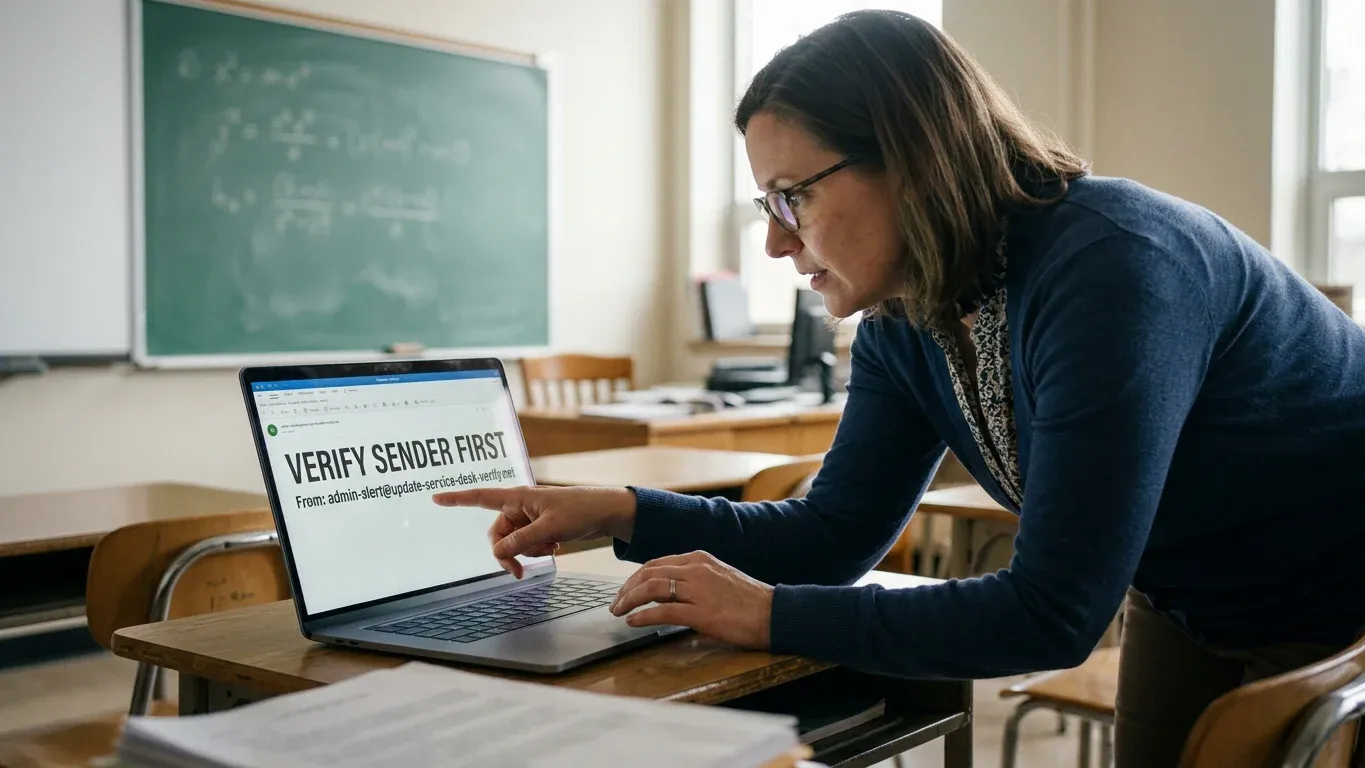
When you know your staff is smart, kind, and stretched thin, seeing teachers fall for phishing can feel personal. The better question is not why a teacher clicked, but what made that fake email feel normal for just long enough.
The usual reasons are simple, human, and very familiar in schools:
- Busyness: The same pace that keeps a school day moving can also make the wrong email look routine.
- Trust: The habit that makes a school community work is also the habit attackers try to borrow.
- Urgency: A message that feels official can push a good teacher past the pause they normally would take.
- Familiar workflows: The most convincing scams often dress up as the tools, vendors, forms, and requests staff already see.
- Training gaps: A click often shows a missing habit, not a missing conscience.
- Shame: When a mistake feels unsafe to admit, the school loses its fastest warning system.
The click is rarely the whole story.
The email did not fool a careless teacher. It caught a busy one.
You are not wrong to feel protective of your staff and worried for the school at the same time. A phishing email works best when it blends into a normal day, not when it looks like a movie villain in a hoodie.
That is why blaming the person usually misses the point. Teachers are not sitting around looking for trouble. They are answering parents, posting assignments, checking attendance, covering recess duty, and trying to remember whether they ate lunch.
A bad click is often a signal, not a character report.
The real danger is treating one hurried action like proof that someone is careless. That shuts down the learning you actually need.
What phishing looks like when it walks into a school
You are usually looking at a fake message that asks a real person to take a real action before they slow down.
Phishing in a school: A deceptive email, text, form, or shared file that pretends to be from a trusted person or system so a staff member will click, sign in, share information, approve a payment, or reply with something sensitive.
In a school, that might look like a password reset, invoice, payroll notice, shared document, parent request, vendor update, substitute system alert, or message that appears to come from leadership.
It is social engineering with a school calendar.
The message does not need to be perfect. It only needs to arrive at the right time, use the right pressure, and look close enough to something your staff already handles.
Why teachers fall for phishing when the day is already moving too fast
You know how quickly a school day can turn from organized to popcorn machine. That pace is one reason teachers fall for phishing, especially when the email asks for a small action that seems routine.
A teacher may click because the message arrives during:
- A passing period
- Morning arrival
- A parent email backlog
- A prep period that is not really a prep period
- The five minutes before dismissal
- A moment when three people need three different things
Phishing takes advantage of shortcuts. In schools, shortcuts are not laziness. They are survival tools.
Think of a phishing email like a bad substitute lesson plan. At first glance, it looks fine. The title is right, the handout is attached, and the directions seem clear. Then period two starts, and you discover the quiz is for the wrong chapter.
Speed is the attacker’s favorite hallway pass.
The fix is not telling teachers to stop being busy. That ship sailed sometime around the first fire drill. The fix is building tiny pause habits into the moments when the day is moving too fast.
The same trust that holds a school together can be borrowed by a scam
You cannot run a school without trust, and that is exactly why attackers try to sound like someone who belongs there.
Schools work because people help quickly. A teacher replies to a parent. An office manager forwards a form. A staff member helps a colleague who says they are locked out. A small private or faith-based school may feel even more personal because people know one another, help one another, and assume good intent.
| School habit | How a scam borrows it |
|---|---|
| Helping a colleague quickly | A fake request asks for gift cards, files, or login help |
| Responding warmly to parents | A message pretends to be a family with an urgent need |
| Respecting leadership | An email uses a principal’s name or tone |
| Working with trusted vendors | A fake invoice looks like normal business |
That trust is beautiful. It also needs guardrails.
The goal is not to make your staff suspicious of everyone. The goal is to help them verify unusual requests without feeling rude.
Urgency makes a fake message feel like a real responsibility
You have probably seen the kind of message that makes a reasonable adult feel like they are already late.
Urgency works because school staff are responsible people. If the email says an account will be locked, a payment is overdue, payroll needs confirmation, or a student-related document needs attention, the instinct is to handle it.
Slow down for these pressure signals:
- Immediate deadline: The message says action must happen now.
- Authority language: It appears to come from a principal, finance office, diocese, association, or platform.
- Account threat: It warns of lockout, deletion, suspension, or lost access.
- Secrecy cue: It asks the recipient not to call or not to tell others.
- Payment pressure: It requests gift cards, wire changes, invoice approval, or new banking details.
Urgency is not proof that the request is real.
Urgent and important are not the same thing. A real issue can wait the thirty seconds it takes to verify through a known channel.
The best scams wear the clothes of ordinary school work
Your staff are more likely to believe a fake message when it looks like the work they already do every week.
The clumsy scams still exist, of course. Somewhere out there, a prince with a suspicious inheritance is still trying his best. But the better scams are quieter. They copy the boring stuff.
Vendor request: A fake invoice or payment change appears to come from a copier company, curriculum vendor, lunch provider, or maintenance contact.
Shared document: A link looks like a lesson file, enrollment form, board document, or collaboration folder.
Password reset: A message claims the teacher’s school account, gradebook, learning platform, or email access is expiring.
Parent message: A note appears to be from a family asking for help, a form, or a quick reply.
Internal leadership name: A scammer uses the principal’s name, a finance phrase, or a familiar signoff to make the request feel official.
The more ordinary the request looks, the less likely the brain is to treat it as a threat.
That is why one generic warning at the start of the year fades so quickly. Staff need practice with examples that feel like their actual inbox.
A click is a training signal, not a scarlet letter
You have a better chance of protecting your school when the response feels like coaching, not a courtroom.
If a teacher clicks a simulation or reports a suspicious email after the fact, the most useful question is simple: What cue did they miss? Maybe it was the sender address. Maybe it was the rushed tone. Maybe it was a login page that looked almost right.
When you need the next step to feel like support instead of scolding, a tool like ThouShaltNotClick can turn that missed cue into targeted practice without making the whole faculty feel blamed.
See the full training program at thoushaltnotclick.com/phishing-training when your goal is to turn a missed cue into calm, trackable staff learning.
This is where the best response changes the story. The click becomes information. The staff member gets practice on the exact kind of threat that fooled them. You get a cleaner way to show that the school responded responsibly.
What this gives a principal:
- Certificates that map to CISA, USCCB, and FERPA frameworks for audit and insurance use
- Training built by Education Technology Professionals, a National Catholic Educational Association Proud Partner
- Content designed by a team with 10+ years supporting K-12 schools of every tradition
That kind of documentation matters when a board, insurer, diocesan office, or professional-development report asks what the school has done beyond sending another reminder email.
Shame is how one mistake becomes a quieter, bigger risk
You lose time when staff are afraid to say they clicked.
Silence is expensive.
Not every click causes the same harm, but every click deserves fast reporting and learning. If people worry they will be embarrassed in front of colleagues, they may wait, delete the message, or hope nothing comes of it.
That is human. It is also risky.
A healthier culture says, report quickly, preserve what happened, and learn from it. Phishing simulations are useful only when they are treated as practice, not as a gotcha.
The safest staff culture is not the one where no one makes mistakes. It is the one where people speak up fast.
What filters and reminders still cannot teach
You should use sensible technical protections and clear rules, but they do not replace human practice.
Filters help. Policies help. Password habits help. Reporting procedures help. But no single layer catches every convincing message, especially when the request looks like normal school business.
| Protection | Helps with | Does not replace training on |
|---|---|---|
| Email filters | Blocking many known bad messages | Spotting the convincing ones that get through |
| Written policies | Setting expectations | Building quick judgment under pressure |
| Staff reminders | Keeping the topic visible | Practicing decisions in realistic moments |
| Simulations | Revealing risky patterns | Teaching without follow-up or context |
| Reporting habits | Speeding up response | Removing the fear that keeps people quiet |
The lesson is not that tools are useless. The lesson is that people need practice too.
That practice should respect the teacher’s day. If training feels like a giant corporate video dropped into a school calendar, your staff will treat it like one more thing done with one eye on the clock.
The next step is practice your staff can actually finish
You are looking for training that fits a school, not a bank, hospital, or corporate office with a whole security department.
School-ready training should be:
- Short enough to finish: Teachers need modules built around the reality that spare time is scarce.
- Relevant to school inboxes: Examples should include phishing, business email compromise, ransomware, fake documents, and school-style requests.
- Respectful in tone: Training should never make a staff member feel foolish for being human.
- Trackable for leadership: Quiz scores and completion records help you answer boards, insurers, diocesan offices, and audit requests.
- Tied to real mistakes: Advanced training should be assigned when someone clicks a simulation, so the learning matches the missed cue.
- Flexible for your community: Content should be able to fit Catholic, Christian, Jewish, Muslim, or fully secular school settings.
- Useful beyond staff email: An Online Kindness module can support student digital citizenship alongside staff cybersecurity learning.
That combination matters because your goal is not to turn teachers into security analysts. Your goal is to help good school people recognize bad messages before a normal habit becomes an expensive problem.
Practice works best when it feels like help, not homework.
Frequently Asked Questions
What should a principal do after a teacher clicks a phishing email?
Start with calm reporting, not blame. Preserve the message if possible, notify the right internal contact, change affected passwords if needed, and document what happened so the school can learn from the pattern.
How often should teachers get phishing training?
Short, regular practice is usually better than one long annual lecture that everyone forgets by October. The right rhythm depends on your school, but the goal is to keep recognition fresh without overwhelming staff.
Are phishing simulations a good idea for school staff?
They can be helpful when they are used as practice, not public embarrassment. A simulation should lead to clear teaching, safe reporting habits, and follow-up support for the people who missed the cue.
Can small private or faith-based schools afford meaningful cybersecurity training?
Meaningful training does not have to look like an enterprise program built for a large corporation. Many small schools need something practical, understandable, and aligned with professional-development or school safety priorities.
What proof should a school keep after cybersecurity training?
Keep completion records, quiz scores, certificates, and any documentation showing what topics were covered. Those records can help when a board, insurer, diocesan office, or auditor asks what steps the school has taken.
A school leader does not need to turn one bad click into a season of staff anxiety. If you want teachers to feel supported while you build a stronger inbox culture, see the full training program at thoushaltnotclick.com/phishing-training.
Business Information Contact Card
Business name: ThouShaltNotClick (TSNC)
Parent Company: Education Technology Professionals, LLC (ETP)
Phone: 1-800-556-1816
Headquarters/Base: Philadelphia area, nationwide service
Website/action URL: thoushaltnotclick.com/phishing-training