Cybersecurity Awareness Habits Busy Teachers Can Keep
You know one ordinary staff email can become a school-wide headache, but cybersecurity awareness cannot become one more heavy binder on a teacher’s already crowded desk. The goal is not to turn…
You know one ordinary staff email can become a school-wide headache, but cybersecurity awareness cannot become one more heavy binder on a teacher’s already crowded desk. The goal is not to turn teachers into IT experts, but to give them habits simple enough to use between dismissal, lunch duty, grading, and parent emails.
- Pause before the click: The smallest habit in the room is often the one that stops the biggest mess.
- Check the sender, not just the name: Scammers count on kindness, speed, and familiar-looking names doing their work for them.
- Treat urgent money requests as a two-step decision: The more rushed the message feels, the more it needs a second channel.
- Make reporting feel safe: Staff will speak up faster when a mistake is treated like a fire drill, not a courtroom.
- Practice with real school scenarios: Awareness sticks better when the scam looks like something that could land in a school inbox.
- Follow up where the click happened: The best teaching moment is the one tied to the exact miss, while it is still fresh.
- Keep proof without chasing paper: A safer staff also needs records a principal can actually produce when asked.
Safer habits only work when they fit the school day, not the other way around.
The Cybersecurity Awareness Habits Teachers Can Actually Keep
A good staff habit has to survive real school life, not a quiet training room that nobody has seen since August in-service. If it takes too long, sounds too technical, or feels like blame, it will fade the moment the bell rings.
The best habits for busy teachers are:
- Quick: usable in seconds, not minutes.
- Repeatable: the same pattern works across many emails.
- Specific: staff know exactly what to look for.
- Kind: mistakes are handled as learning moments.
- Documented: the school can show what training happened.
The habit that works is usually the one a teacher can remember between two bells.
No, teachers are not the problem. Scammers design messages to exploit normal helpfulness and hurry, which are two things schools have in abundance.
And no, awareness does not replace technical security tools. Awareness is one layer, not the whole lock on the door.
The Tiny Pause That Gives a Teacher’s Brain Time to Catch Up
The pause works because phishing depends on motion. A teacher sees a message, feels the nudge, and clicks before the thinking part of the brain has had a fair turn.
That pause does not need to be dramatic. Nobody has to stare at the screen like a detective in a raincoat. The point is to create one small speed bump before the action.
- Links: Does the destination look expected, or does it feel slightly off?
- Attachments: Was this file expected, and does the file type make sense?
- Login prompts: Is the email pushing staff to sign in from a link?
- Unexpected urgency: Is the message trying to make thinking feel irresponsible?
A pause is not paranoia. It is a seat belt for the inbox.
This is the first habit because it gives every other habit room to work. Once staff slow down, they can check the sender, question the request, and report uncertainty before a small click becomes a long afternoon.
The Name on the Email Is Not the Same as the Sender
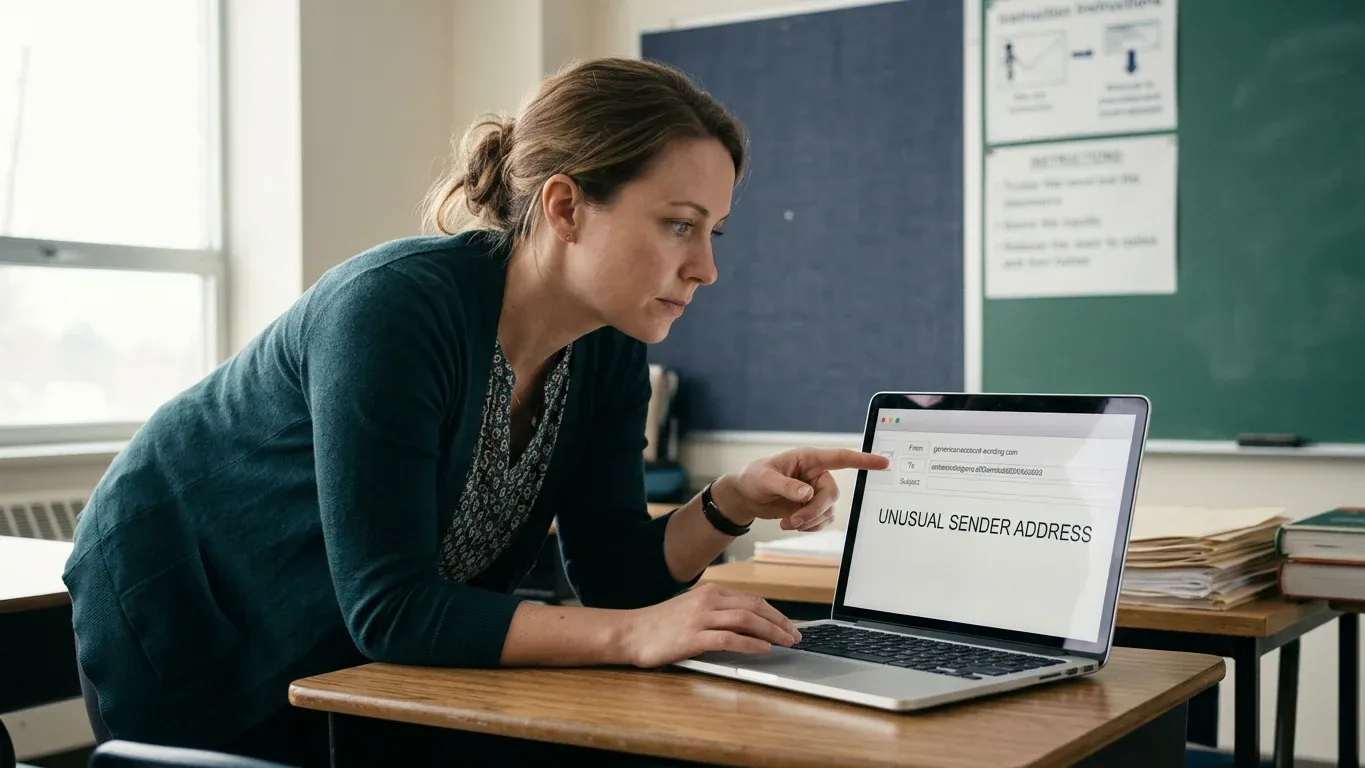
Your teachers see familiar names all day, so a familiar display name can feel safe before anyone looks closer. That is exactly what many scams count on.
A display name is like a name tag at a conference. Helpful, yes, but not the same as checking who is actually wearing it.
Staff do not need to become email-forensics experts. They just need to know that the name they see first may not match the real sending address, especially on a phone where details are hidden.
A practical sender-check habit sounds like this: “Before I open the attachment or follow the link, I check whether the address matches the person or organization I expected.” That one sentence catches a lot of trouble.
It also protects the kindest people on staff. The teacher who wants to help quickly is often the person most likely to respond to a fake principal, fake parent, fake vendor, or fake diocesan message.
When Money Sounds Urgent, Slow the Whole Room Down
Money requests deserve their own rule because they create a special kind of pressure. A fake gift-card request that looks like it came from the principal can make a generous staff member feel helpful, loyal, and rushed all at once.
Phishing is often a broad attempt to trick someone into clicking, signing in, or sharing information. Business email compromise, often called BEC, is more focused: it uses a trusted business or leadership identity to push payment, gift cards, account changes, or sensitive action.
| Message pressure | Safer staff habit | Principal’s rule of thumb |
|---|---|---|
| Gift cards | Stop and verify by phone or in person | No urgent gift-card purchase starts from email alone |
| Wire or payment changes | Use a known contact method, not the one inside the email | Payment changes need a second channel every time |
| Password reset | Go directly to the known site instead of using the email link | Login links should not be trusted just because they look polished |
| Document share | Ask whether the file was expected before opening | Surprise documents deserve a second look |
The more an email tries to rush the decision, the more the school should slow the decision down.
This is not about making staff suspicious of every message from leadership. It is about giving them permission to verify, even when the request appears to come from someone important.
A Good Reporting Culture Beats a Perfect Lecture
Staff report faster when they believe the school wants the truth more than it wants someone to blame. That matters because a quick report can limit confusion, warn others, and help the right person respond.
Reporting speed matters more than embarrassment, because silence gives the scam more room to move.
A safe reporting norm sounds like:
- “If something feels off, send it in.”
- “If you clicked, tell us quickly so we can help.”
- “You will not be shamed for asking.”
- “We would rather check ten harmless emails than miss one dangerous one.”
That tone is not soft. It is practical. A courtroom mood makes people hide mistakes, while a fire-drill mood helps everyone move quickly and calmly.
The principal sets this culture in small ways. A thank-you after a report, a calm response after a mistake, and a clear process for suspicious emails all teach staff what the school really values.
Cybersecurity Awareness Works Better When It Sounds Like School
Teachers can smell generic training from across the faculty room. If the examples all sound like a bank, a hospital, or a corporate office with three legal departments, staff may finish the module and still miss the scam aimed at your school.
School-shaped training makes the lesson harder to dismiss because the inbox feels familiar.
Useful examples should sound like the work your staff already does: tuition questions, parent messages, substitute plans, shared documents, vendor invoices, diocesan notes, and leadership requests that arrive at exactly the wrong moment.
When your staff need practice that sounds like a school day instead of a corporate policy manual, ThouShaltNotClick’s training approach matters because it was built around real K-12 staff habits, not abstract office life. Its Cybersecurity Training Courses include six built-in modules covering phishing, business email compromise, ransomware, and more, with content written to respect how little spare time a busy teacher has.
Faith fit can matter here too. Some schools need training that can speak naturally inside a Catholic, Christian, Jewish, Muslim, or secular environment without feeling pasted on. Student digital citizenship belongs nearby, but it is not the same job: students need age-appropriate online kindness and digital behavior lessons, while staff awareness protects accounts, data, and school workflows.
Relevance is not decoration. It is how the lesson gets past the eye roll.
The Missed Click Is Where the Better Lesson Starts
A simulation click should not end with a spreadsheet, a sigh, or a vague reminder at the next faculty meeting. The useful question is simple: what did this person miss, and how can the school teach that point while it is still fresh?
Targeted follow-up keeps training from becoming a lecture tour
General reminders have their place, but they often land on everyone equally, including people who did not need that lesson that day. Targeted follow-up connects the training to the exact behavior that showed up in practice.
After staff are enrolled through an Organization account, each person can work through interactive course modules at their own pace, complete a quiz, and receive a recorded certificate when finished. In the same training system, advanced training is automatically assigned to staff who click a simulation, which closes the loop without the principal manually chasing every follow-up.
No lecture tour. No public shaming.
That distinction matters. A missed click is not proof that a teacher is careless. It is proof that one scam pattern was convincing enough to deserve a better lesson.
The Habit Principals Forget: Keep the Receipts
You may be thinking about safer clicks, but your board, insurer, diocesan office, or auditor may ask a different question: can you prove staff completed the training? That is where many good intentions turn into a paper chase.
Completion proof is not busywork when it saves you from digging through emails the night before a report is due. Quiz scores and certificates help show that training happened, who completed it, and where follow-up may be needed.
What the principal can show
- Auto-issued completion certificates for finished courses
- Quiz scores recorded per staff member
- Certificates mapped to CISA, USCCB, and FERPA frameworks for audit and insurance use
- Training content designed by a team with 10+ years supporting K-12 schools of every tradition
- Support from Education Technology Professionals, a National Catholic Educational Association Proud Partner
This is where the burden question finally gets answered. Cybersecurity awareness becomes manageable when the program does not depend on the principal remembering every reminder, finding every certificate, and matching every missed click with the right follow-up.
If you want to compare what a school-shaped training program includes, you can see the full training program at thoushaltnotclick.com/phishing-training, or start free as a teacher at thoushaltnotclick.com/signup/teacher.
The pricing question matters in small and mid-sized schools, especially when budgets are fixed long before the next scam arrives. The Organization plan is listed at $5 per staff member per month, with a 20-staff minimum and $100 per month floor, and schools can pay by card monthly or invoice annually. The offering is also fundable through Title II-A professional-development funds and Title IV-A.
Basic training is available free to the first teacher at a school, which gives a small school a way to start without pretending it has a giant IT department hiding in the supply closet.
The real win is not louder training. It is quieter confidence.
Frequently Asked Questions
What is cybersecurity awareness in a school?
Cybersecurity awareness in a school means staff know how to spot and report common digital risks, especially suspicious emails, fake login pages, urgent payment requests, and unsafe attachments. It turns security from an IT-only concern into everyday habits teachers and administrators can actually use.
How often should teachers get cybersecurity awareness training?
Most schools benefit from regular, short refreshers rather than one long annual session that everyone forgets by October. The key is to keep training practical, current, and tied to the kinds of messages staff actually receive.
Is cybersecurity awareness enough to protect a school?
No. Awareness is one important layer, but schools also need appropriate technical safeguards, good account practices, clear reporting paths, and leadership support. Think of awareness as the human layer that helps the rest of the system work better.
What should a teacher do after clicking a suspicious link?
The teacher should report it right away to the school’s designated contact and avoid trying to hide or “fix” it alone. Fast reporting gives the school a better chance to respond, check affected accounts, and warn others if needed.
Can cybersecurity training count as professional development?
Cybersecurity training can fit naturally into professional development when it teaches staff skills they need to protect school systems, student information, and daily operations. Some offerings are fundable through professional-development sources, so school leaders should check how the training maps to their own reporting needs.
How can a small school start without a big IT staff?
Start with a few clear habits: pause before clicking, verify urgent requests through a second channel, report suspicious messages quickly, and keep records of completed training. A simple, documented program is far better than a complex plan nobody has time to run.
Safer staff email habits do not have to become another stack on your desk; they should make the school day a little calmer because people know what to do. If you want training built for real school staff, see the full program at thoushaltnotclick.com/phishing-training or start free as a teacher at thoushaltnotclick.com/signup/teacher.
ThouShaltNotClick
Phone: 1-800-556-1816
Address: Philadelphia area (nationwide service)